Home » Featured partners » eSentire

eSentire is a managed detection and response provider that catches and deals with threats around the clock. It pairs AI with a 24/7 expert human team that finds weaknesses before attackers do and stops threats in real time.
Runs 24/7 • Works across your existing stack
eSentire was founded in 2001 by Eldon Sprickerhoff, the person widely credited with inventing managed detection and response, and MDR is still the whole business. It now protects 2,000+ organisations across more than 35 industries worldwide.
That focus is why eSentire sits on our featured partner list. Its service does the part most tools leave to you: rather than firing an alert and waiting for someone to notice, a 24/7 expert team hunts, investigates and contains threats around the clock.
It works across the security tools our clients already run, so detection improves without ripping anything out, and that track record on something as critical as threat response is why we trust it.
– Founded in 2001, the original pioneer of managed detection and response
– AI plus a 24/7 expert human SOC, hunting, investigating and containing threats in real time
– Protects 2,000+ organisations across 35+ industries worldwide
eSentire's pitch for 2026 is that detection, response and offence work better as one loop than as separate tools: testing finds the gaps, detection catches what gets through, and response shuts it down, each step making the next one sharper.
Autonomously stress-test your environment through the attacker's lens.
Detect and respond across any stack and every signal.
Stop attackers and reduce your attack surface so you're harder to hit next time.
Atlas powers Controlled Autonomy SecOps, connecting your entire stack and enriching every signal with over two decades of experience and elite AI operatives. No signal ignored.
Atlas runs 24/7 detection and probes for gaps continuously. No quarterly assessments. No scan schedules.
Atlas continuously adapts your security program, from offensive findings that improve detection, detections that accelerate response, and response that stops attackers.
Atlas contains threats and adapts at machine speed, validates controls continuously, and closes the paths attackers would take next.
Atlas simultaneously ingests from SentinelOne, Microsoft Defender, CrowdStrike, and more. Enriched intelligence flows back to every tool.
Knowing which AI tools your people use is the easy part. AI coding assistants and agents work with real credentials and broad permissions, often pulling in third-party MCP servers, touching code and data and acting on their own.
Atlas AIDR turns every AI session into an attributable record tied to a user, team and workstation, screens prompts for secrets, personal data and prompt injection, and applies redaction and block rules inline. If something needs attention, the same 24/7 SOC that watches the rest of your estate investigates and responds.
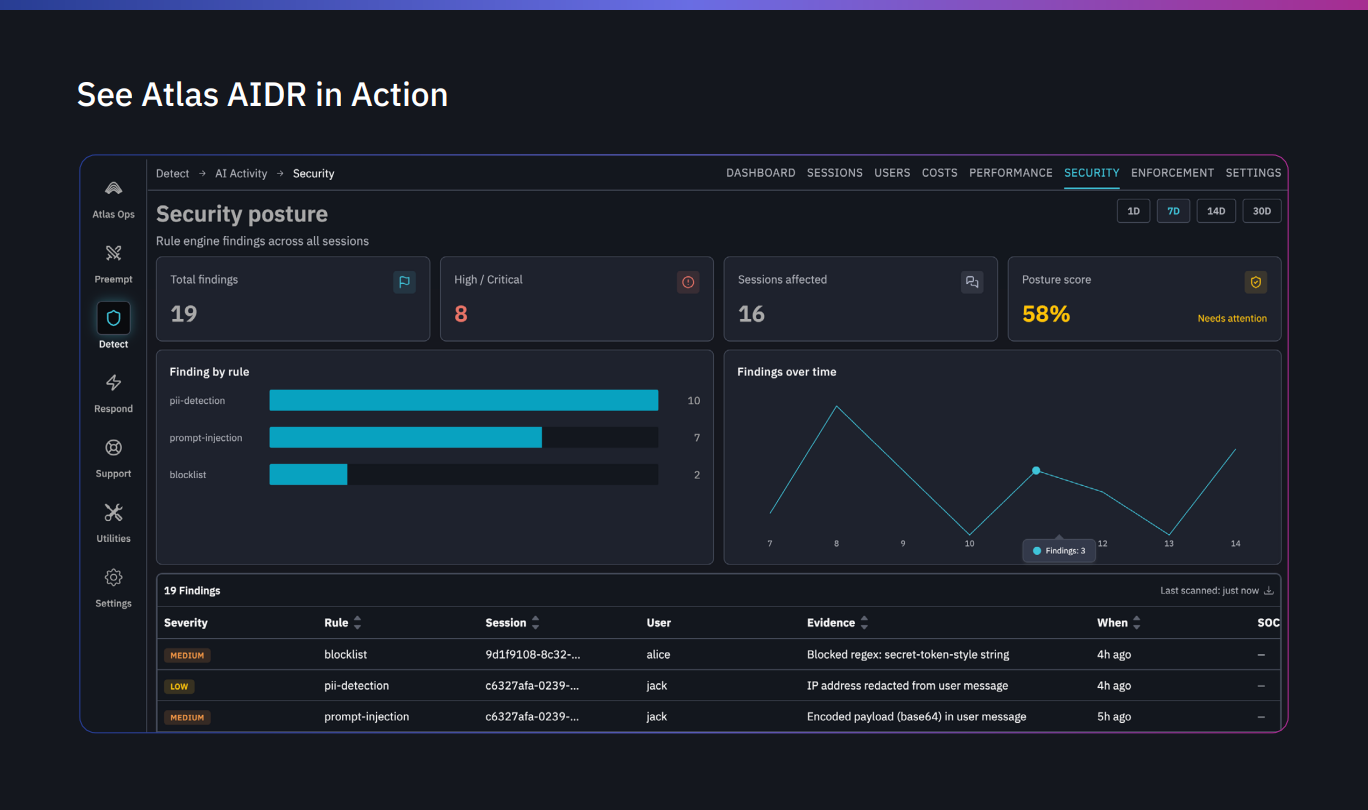
It covers Anthropic, OpenAI, Google and Amazon Bedrock as model providers, with native depth for Claude Code, Cursor, GitHub Copilot, Codex and Gemini CLI. No rip and replace required.
Ask us about Atlas AIDR.
Highgate configures and manages your eSentire deployment as part of our cybersecurity service, with a named account manager who turns an alert into action rather than leaving you to read a dashboard. It sits inside the same ISO 27001 and Cyber Essentials Plus certified service that covers the rest of your estate.

In our experience, it earns its place fastest for organisations without a 24/7 in-house security team, those in regulated or compliance-driven sectors, and anyone running several security tools they want unified rather than watched separately. If you already have a mature round-the-clock SOC, we'll tell you honestly where MDR adds to it and where it doesn't.
No. eSentire works across the stack you already run, from SentinelOne to Microsoft Defender to CrowdStrike, enriching what those tools see rather than replacing them. You get better detection without ripping anything out.
Tell us a little about your organisation and one of our team will come back to you.